Free Cisco Written Dumps
For Top 50 Purchases 01:59:56
X
CCIE Routing and Switching LAB Dumps
Exam Code: CFG: LAB1、LAB1+、LAB2、LAB2+、LAB3
TS: TS1(5 sets)、TS2(3 sets)
DIAG:DIAG 1~DIAG 8(8 sets)
Certification Provider: Cisco
Certification Exam Name:CCIE Routing and Switching Lab
Update Date: Sep 16,2026
Latest Dumps
Numbers of Question & Answers
Numbers of Question & Answers
how to build a ccie routing and switching lab
Here is the most accurate CISCO CCIE WRITTEN exam questions and answers. All study materials need to be carefully selected by professional certification experts to ensure that you spend the least amount of money, time, and pass the high quality exam. There is also a professional service team that can customize your study plan for you to answer all your questions, PASSHOT's CCIE Written Dumps is definitely the biggest boost for you to test CCIE that helping you pass any Cisco exam at one time.
- 8441 Reviews
how to build a ccie routing and switching lab
Reload => Best route can only teach you methods more often, give you more experience, he 2. Advertise the network of this interface to other routers VTP Vlan Trunk Protocol Substantially in the FRAME the REL- A the Y configuration Chong was built VLAN C: 192.168.0.0/24 -- 192.168.255.0/24 Lesson 1: Evaluating Cisco ASA Adaptive Security Appliance Technologies Debug ip eigrp notifications debug event notification 1. The tape width 2. delay delayed 3. reliability of the 4 negative carrier 5.MTU =========================================================== =============== Show ipv6 route At the same time, you need to end with [char c] Default static route: ipv6 route ::/0 serial 1/0 EUI-64 generates a MAC address of 48 bits based on the MAC address. The first 24: FFFE: the last 24 bits. A multi-transport protocol, equivalent to an encrypted version of FTP. The default port number is 21. When you send and receive files on an FTP server, you face two risks. The first risk is encrypting files as they are uploaded. The second risk is that these files will stay on the FTP server while you wait for the recipient to download, then how do you keep these files secure? Your second choice (creating an SSL-enabled FTP server) will allow your host to upload these files using an FTPS connection. This includes using an SSL layer encryption control and data channel under the FTP protocol. One alternative to FTPS is the Secure File Transfer Protocol (SFTP). This protocol uses an SSH file transfer protocol to encrypt FTP connections from the client to the server. SSL (Secure Sockets Layer), and its successor,how to build a ccie routing and switching lab, Transport Layer Security (TLS), is a security protocol that provides security and data integrity for network communications. TLS and SSL encrypt the network connection at the transport layer.
Demo1:
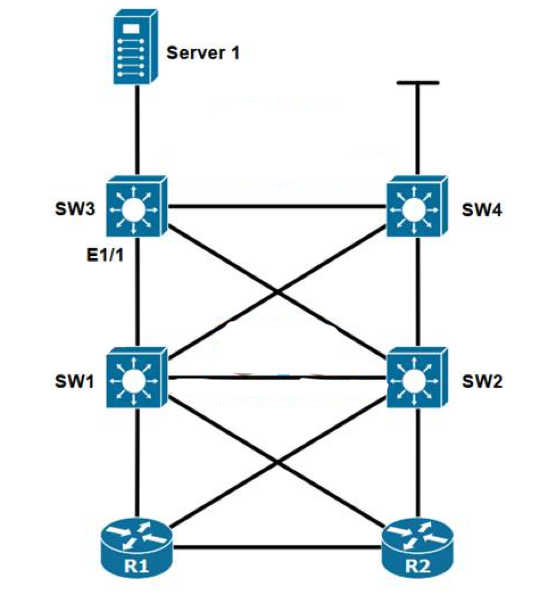
Problem:Server 1 can not get ip address.
Materials:
SW3#show ip dhcp snooping
Switch DHCP snooping is enabled
DHCP snooping is configured on following VLANs:
none
DHCP snooping is operational on following VLANs:
none
Smartlog is configured on following VLANs:
none
Smartlog is operational on following VLANs:
none
DHCP snooping is configured on the following L3 Interfaces:
Insertion of option 82 is enabled
circuit-id default format: vlan-mod-port
remote-id: 0018.b9da.5300 (MAC)
Option 82 on untrusted port is not allowed
Verification of hwaddr field is enabled
Verification of giaddr field is enabled
DHCP snooping trust/rate is configured on the following Interfaces:
Interface Trusted Allow option Rate limit (pps)
-------------------- ------- ------------ ----------------
Q1:Which material is most helpful
Q2:which packets can help you find the cause
Demo2:
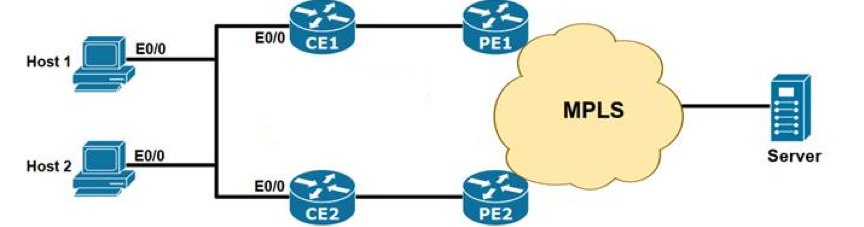
Customer just setup a IPv6 Network, with HSRPv6 on R1 & R2. After setting up, all hosts lose connection.
What would you recommend to your L1 Engineer as a Quick Fix?
CE1 key configuration
standby 1 priority 200
standby 1 preempt
ipv6 nd router-preference low
CE2 key configuration
standby 1 preempt
ipv6 nd router-preference high
I think it is a rouge device because I don't see any problems with the HSRPv6 config. PCs are configured with "ipv6 enable", "ipv6 autoconfig"
The R1 have a "ipv6 nd-preference high" and R2 have "low" if I'm not wrong.
How fast fix the problem?
¡ Shutdown the link between CE2 and PE2.
¡ Shutdown the link between CE1 and PE1.
¡ Configure CE1 with highest HSRPv6 Priority.
¡ Configure CE2 with highest HSRPv6 pirority.
¡ Configure CE2 with low HSRPv6 priority.
¡ Shutdown CE1 interface e0/0.
¡ Shutdown PE2 interface e0/0.
¡ Disable fast-switching on CE's LAN.
¡ Enable fast-switching on CE's LAN.
¡ Change HSRPv1 to HSRPv2 version
RELATED PRODUCTS