Free Cisco Written Dumps
For Top 50 Purchases 01:59:56
X
CCIE Routing and Switching LAB Dumps
Exam Code: CFG: LAB1、LAB1+、LAB2、LAB2+、LAB3
TS: TS1(5 sets)、TS2(3 sets)
DIAG:DIAG 1~DIAG 8(8 sets)
Certification Provider: Cisco
Certification Exam Name:CCIE Routing and Switching Lab
Update Date: Sep 16,2026
Latest Dumps
Numbers of Question & Answers
Numbers of Question & Answers
- 4135 Reviews
ccie security
End 1. Add this interface to the rip process. Change console baud rate? y/n [n]: y (select yes) 1. Content of the announcement : incremental update (OSPF lsa) 2. Announcement time : Trigger 3. Announced object : Has neighbor relationship Configuring and Verifying Transparent Firewall Mode Assigned for this sub-specific interfaces of PVC. ??? is a PVC number . Switchport access vlan 10 The SSL/TLS protocol works on top of the transport layer (TCP/IP) but below the application layer. Therefore, it can be easily implemented on application layer protocols such as HTTP, Telnet, POP3, IMAP4, SMTP and FTP. There are at least two different initialization methods for SSL security extensions: explicit security and implicit security. B(config)#access-list 1 permit any "Good. You can accept the black belt and start fighting." FTPS is an enhanced FTP protocol that uses standard FTP protocols and commands at the Secure Sockets Layer to add SSL security to the FTP protocol and data channels. FTPS is also called "FTP-SSL" and "FTP-over-SSL". SSL is a protocol that encrypts and decrypts data in a secure connection between a client and an SSL-enabled server. (-) Network equipment manufacturer Three forwarding modes of the switch : Source : The case of Access dial is the most feared contact I made when I was an engineer at TAC, so I had to learn more about it - this is what forced me to learn the knowledge rather than the ISP Dial CCIE qualification. A better way. It is also a good way to learn about IBM technology. When I became a SiS engineer, the IT industry was at the end of the transition from SNA to IP. As a DS engineer, I have some calls for help. I am afraid to answer, because I am a relatively ''new age'' network learner and have never been exposed to FEPs, mainframes, etc. thing. Again, this is a good way to drive me to learn the relevant knowledge, not to achieve SNA IP CCIE eligibility. As for the Security (network security) CCIE, I have repeatedly learned about security and CiscoSecure ACS to cope with the ISP Dial exam. In addition, in order to prepare for the CCIE design exam, I also learned a lot of security knowledge. After the end of the fall professional sports league program,ccie security, I began to review what I had learned before, and also learned some new cybersecurity knowledge to make up for my lack of knowledge about cybersecurity. As for the rest, because it is not important, I will not go into details.
ccie security
Here is the most accurate CISCO CCIE WRITTEN exam questions and answers. All study materials need to be carefully selected by professional certification experts to ensure that you spend the least amount of money, time, and pass the high quality exam. There is also a professional service team that can customize your study plan for you to answer all your questions, PASSHOT's CCIE Written Dumps is definitely the biggest boost for you to test CCIE that helping you pass any Cisco exam at one time.
Demo1:
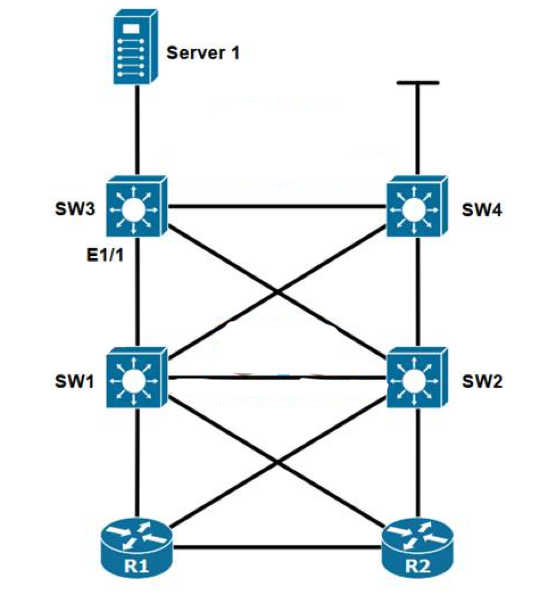
Problem:Server 1 can not get ip address.
Materials:
SW3#show ip dhcp snooping
Switch DHCP snooping is enabled
DHCP snooping is configured on following VLANs:
none
DHCP snooping is operational on following VLANs:
none
Smartlog is configured on following VLANs:
none
Smartlog is operational on following VLANs:
none
DHCP snooping is configured on the following L3 Interfaces:
Insertion of option 82 is enabled
circuit-id default format: vlan-mod-port
remote-id: 0018.b9da.5300 (MAC)
Option 82 on untrusted port is not allowed
Verification of hwaddr field is enabled
Verification of giaddr field is enabled
DHCP snooping trust/rate is configured on the following Interfaces:
Interface Trusted Allow option Rate limit (pps)
-------------------- ------- ------------ ----------------
Q1:Which material is most helpful
Q2:which packets can help you find the cause
Demo2:
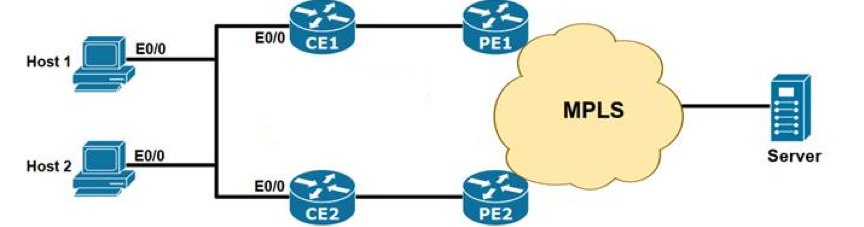
Customer just setup a IPv6 Network, with HSRPv6 on R1 & R2. After setting up, all hosts lose connection.
What would you recommend to your L1 Engineer as a Quick Fix?
CE1 key configuration
standby 1 priority 200
standby 1 preempt
ipv6 nd router-preference low
CE2 key configuration
standby 1 preempt
ipv6 nd router-preference high
I think it is a rouge device because I don't see any problems with the HSRPv6 config. PCs are configured with "ipv6 enable", "ipv6 autoconfig"
The R1 have a "ipv6 nd-preference high" and R2 have "low" if I'm not wrong.
How fast fix the problem?
¡ Shutdown the link between CE2 and PE2.
¡ Shutdown the link between CE1 and PE1.
¡ Configure CE1 with highest HSRPv6 Priority.
¡ Configure CE2 with highest HSRPv6 pirority.
¡ Configure CE2 with low HSRPv6 priority.
¡ Shutdown CE1 interface e0/0.
¡ Shutdown PE2 interface e0/0.
¡ Disable fast-switching on CE's LAN.
¡ Enable fast-switching on CE's LAN.
¡ Change HSRPv1 to HSRPv2 version
RELATED PRODUCTS