Free Cisco Written Dumps
For Top 50 Purchases 01:59:56

X
ccie lab time

    ccie lab time

  • 4654 Reviews
  • Note: If the error message is not executed during the transmission, use the command sync to save the configuration. After restarting the router (preferably turn off the power), you can execute the tftpdnld command. +   0x1 Router will add to the load mini ios software , enter the BOOT model    =========================================================== ===================   In fact, the application of in and out is very flexible. Enable secret   In IPV6, a port can participate in different protocols or participate in different processes of the same protocol. 2.CHAP: Challenge-style three-way handshake , password mining with HASH transmission algorithm , than P A P stronger   Configuring Object (Auto) NAT IGRP uses composite metrics to select the best route .      Interface Serial0   real ccie value, borrow a netizen's words: "Huangsha hundred wars wear such ability, there is no such thing as a foothold in the IT world. At NA: Source IP is 2001::1 Destination IP is FF02::1:FF00:0001 To solve the horizontal separation, you can use the sub-interface method.   2.0.0.0   The CISCO 1900 series switches use free shard forwarding to forward this forwarding method by default.    Serial1 is up, line protocol is down   1   10. What are the common BGP routing principles? How to use one piece between the backbone network and the metropolitan area network? Tuning and Managing Active/Active Failover VLAN characteristics   Forced interruption of "telnet to local " session   Consult the version of the exam of other institutions: Configuring and Verifying Cut-Through Proxy Authentication as you are willing to go, as long as you don't give up. My The fourth place of the TR: R19's DM*** IPSEC strategy (I have a XXX!!), quite cute! ! ! Router-id 2.2.2.2 Tunnel mode ipv6ip/gre/ipv6ip auto/ipv6ip isatap/ipv6ip 6to4 Rommon2>xmodem –c c3825-spservicesk9-mz.150-1.M.bin Backplane bandwidth and port speed are the main performance indicators of the switch.   First, key terms Vtp pruning   IPV6 address type: unicast, multicast, anycast I Note :   Disable "load rom after netboot fails"? y/n [n]: n (select no) 1.A vlan == A broadcast domain == A logic subnet   =========================================================== ===============   Debug ppp authentication     Of course, it is difficult for anyone who has entered the society to avoid the “operator” stage, but you have to learn, grow up, people go high, and the water flows down! 1. Switch and bridge   7. When to disconnect     Because each protocol layer on the receiving device needs different information to process the received data, each layer on the transmitting device encapsulates the header information of the response. 7:45 AM and other teachers Protocol data unit   RIP supplement :   Rommon5>DEFAULT_GATEWAY=10.10.22.2 (default gateway, is the address of the PC < time >   Cisco will soon announce the blueprints for the B(config)#inte s 0   than 4k, but fortunately I didn't find bible to cope with the The fourth place of the TR: R19's DM*** IPSEC strategy (I have a XXX!!), quite cute! ! !   4. What are the advantages and disadvantages of UDP compared to TCP? 1) The root port does not participate in the competition of the specified port      Vtp server   Firewall Technologies a) Unicast unicast   3. MPLS L3 ***, what if I want two different *** to be one-way visits? =========================================================== ===============   Troubleshooting Application Layer Inspection Note 2: After transmitting the IOS, you must enter the monitoring mode to change the rate back to the original 9600. Change the transmission rate of the terminal back to the original 9600, and restart it. RA:   FRAME-REL A Y   Dynamic Routing Show cdp neighbors   Fix: Reconfigured, also repeated s version /no s version, or not. In the end, I was courageous and reloaded R17 directly. Now I think it is terrible. Restart the card for nearly 4 minutes, but fortunately dm*** is fine. Finally, don't continue to do it, give up directly! * Confirmed various configurations, IGP, NAT, SW3/SW4 track has not been restored! Especially pay attention! !    Target port :   3. Q993A   b) multicast address Friends who are studying the security direction of CCIE definitely have some understanding of URPF technology, so today we will explain the URPF technology.I. Introduction to URPF TechnologyGenerally, after receiving the data packet, the router obtains the destination IP address in the data packet, searches the local routing forwarding table for the destination IP address, and forwards the data packet if there is a corresponding forwarding entry; otherwise, discards the packet. . From this point of view, when the router forwards the message,ccie lab time, it does not care about the source address of the packet. This gives the source address spoofing attack a chance.The source address spoofing attack constructs a series of packets with the spoofed source address and frequently accesses the device or host where the destination address resides. Even if the response packet cannot reach the attacker, the attacker will cause a certain degree of damage to the attacked object.The main function of unicast reverse path forwarding (URPF) is to prevent network attack behavior based on source address spoofing. After the URPF function is enabled on the interface of the router, when the interface receives the data packet, it checks the legality of the source address of the data packet. The forwarding entry of the address enters the packet forwarding process; otherwise, the packet is discarded.Second, the working mechanism of URPFThe URPF checks the legality of the source address of the packet into strict (strict) and loose (loose) types:Strict-type URPF: not only requires the router to forward the table, but also has a route to the source address of the packet. It also requires that the inbound interface of the packet is the same as the outgoing interface to the source address. The message is considered to be a legitimate message. In some special cases (such as the existence of asymmetric paths), strict type checking will incorrectly discard non-attack messages.
CCIE Routing and Switching LAB Dumps

( 2 People are currently looking at this product )

Exam Code: CFG: LAB1、LAB1+、LAB2、LAB2+、LAB3
TS: TS1(5 sets)、TS2(3 sets)
DIAG:DIAG 1~DIAG 8(8 sets)

Certification Provider: Cisco

Certification Exam Name:CCIE Routing and Switching Lab

Update Date: Sep 16,2026

Free Cisco Written Dumps
For Top 50 Purchases
Latest Dumps
Numbers of Question & Answers

Demo1:

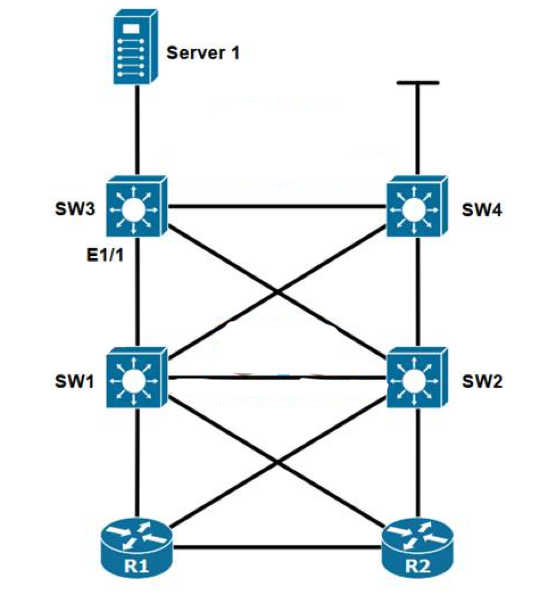
ProblemServer 1 can not get ip address.

Materials:

SW3#show ip dhcp snooping  

Switch DHCP snooping is enabled

DHCP snooping is configured on following VLANs:

none

DHCP snooping is operational on following VLANs:

none

Smartlog is configured on following VLANs:

none

Smartlog is operational on following VLANs:

none

DHCP snooping is configured on the following L3 Interfaces:

Insertion of option 82 is enabled

   circuit-id default format: vlan-mod-port

   remote-id: 0018.b9da.5300 (MAC)

Option 82 on untrusted port is not allowed

Verification of hwaddr field is enabled

Verification of giaddr field is enabled

DHCP snooping trust/rate is configured on the following Interfaces:


Interface          Trusted     Allow option     Rate limit (pps)

 --------------------   -------         ------------     ----------------  

Q1Which material is most helpful

Q2:which packets can help you find the cause


Demo2:
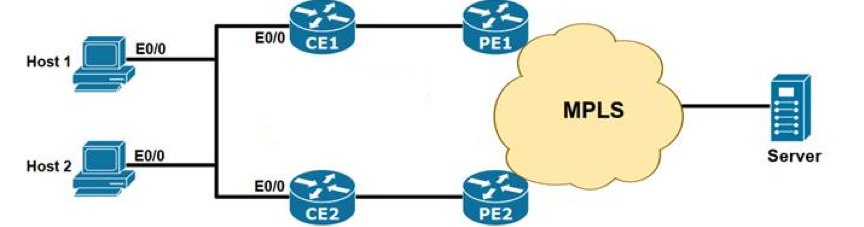
Customer just setup a IPv6 Network, with HSRPv6 on R1 & R2. After setting up, all hosts lose connection.

What would you recommend to your L1 Engineer as a Quick Fix?

CE1 key configuration

standby 1 priority 200

standby 1 preempt

ipv6 nd router-preference low

CE2 key configuration

standby 1 preempt

ipv6 nd router-preference high 


I think it is a rouge device because I don't see any problems with the HSRPv6 config. PCs are configured with "ipv6 enable", "ipv6 autoconfig"

The R1 have a "ipv6 nd-preference high" and R2 have "low" if I'm not wrong.


How fast fix the problem?


¡ Shutdown the link between CE2 and PE2.

¡ Shutdown the link between CE1 and PE1.

¡ Configure CE1 with highest HSRPv6 Priority.

¡ Configure CE2 with highest HSRPv6 pirority.

¡ Configure CE2 with low HSRPv6 priority.

¡ Shutdown CE1 interface e0/0.

¡ Shutdown PE2 interface e0/0.

¡ Disable fast-switching on CE's LAN.

¡ Enable fast-switching on CE's LAN.

¡ Change HSRPv1 to HSRPv2 version


ccie lab time


Here is the most accurate CISCO CCIE WRITTEN exam questions and answers. All study materials need to be carefully selected by professional certification experts to ensure that you spend the least amount of money, time, and pass the high quality exam. There is also a professional service team that can customize your study plan for you to answer all your questions, PASSHOT's CCIE Written Dumps is definitely the biggest boost for you to test CCIE that helping you pass any Cisco exam at one time.

Have any question for us?

Cisco Dumps Popular Search:

ccie security written exam preparation ccna vce dumps 2018 certcollection pcnse ccna 200 120 syllabus pdf ccna question bank ccnp route modules cisco ccna answers ccnp route exam cost uk ccnp route version 7 ccnp switch exam booking

Copyright © 2026 PASSHOT All rights reserved.